Fragmented truth
SIEM, EDR, cloud posture, vulnerability management, identity, email, threat intel and AI systems each hold a slice of your risk. Nothing correlates across all of them.
Security posture · Compliance · AI governance
SOC360.AI is the read-only layer that aggregates every security tool, team and AI system you already own — and turns them into one clear picture of risk for your executives, board, regulators and customers.
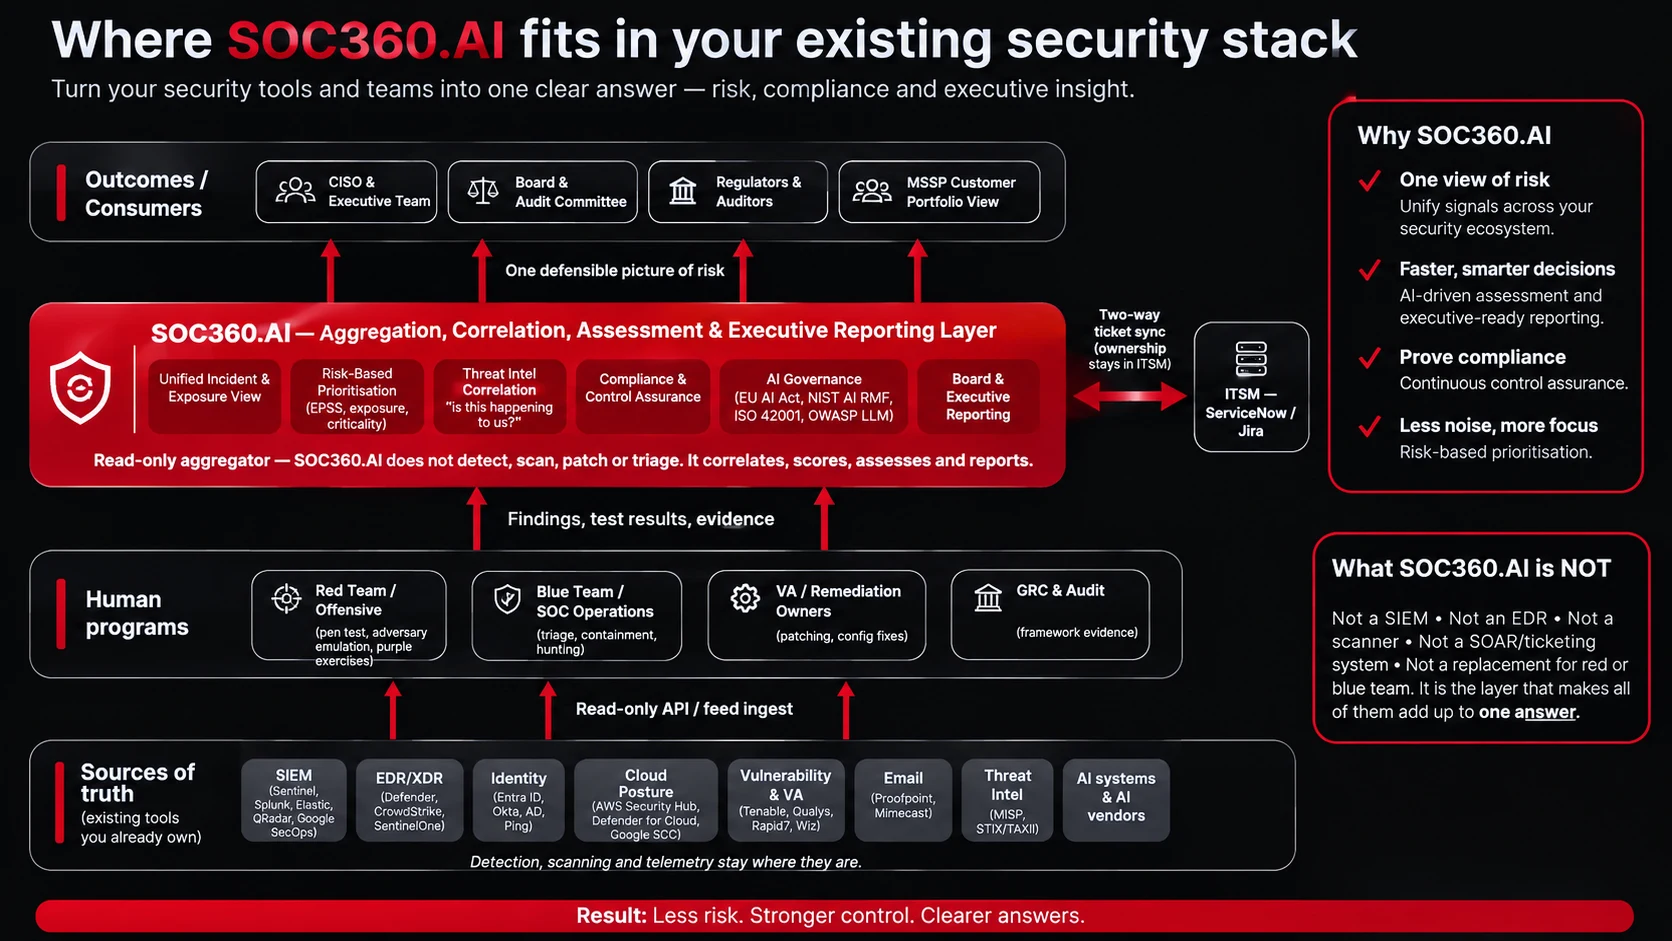
Connects read-only to the stack you already run
The problem
You already own detection, scanning and response. What you can't buy off the shelf is a single, defensible answer.
40+
security tools in a typical enterprise stack, each with its own console, its own score and its own export.
0
of those tools can answer the board's real question: “Are we OK — and can you prove it?”
Weeks
of analyst time burned every quarter stitching screenshots into board packs and audit evidence.
SIEM, EDR, cloud posture, vulnerability management, identity, email, threat intel and AI systems each hold a slice of your risk. Nothing correlates across all of them.
Red team findings, SOC incidents, patch queues and audit evidence live in different tools, owned by different teams, on different clocks.
Boards, regulators and cyber insurers now demand evidence — NIS2, DORA, SEC cyber rules and the EU AI Act all assume you can produce it on request.
AI systems and AI vendors enter the environment faster than any spreadsheet can track them, and your security tools do not see them at all.
Where we fit
SOC360.AI doesn't replace anything. It sits above your existing tools and programs, ingests what they already produce, and turns it into one defensible picture of risk.
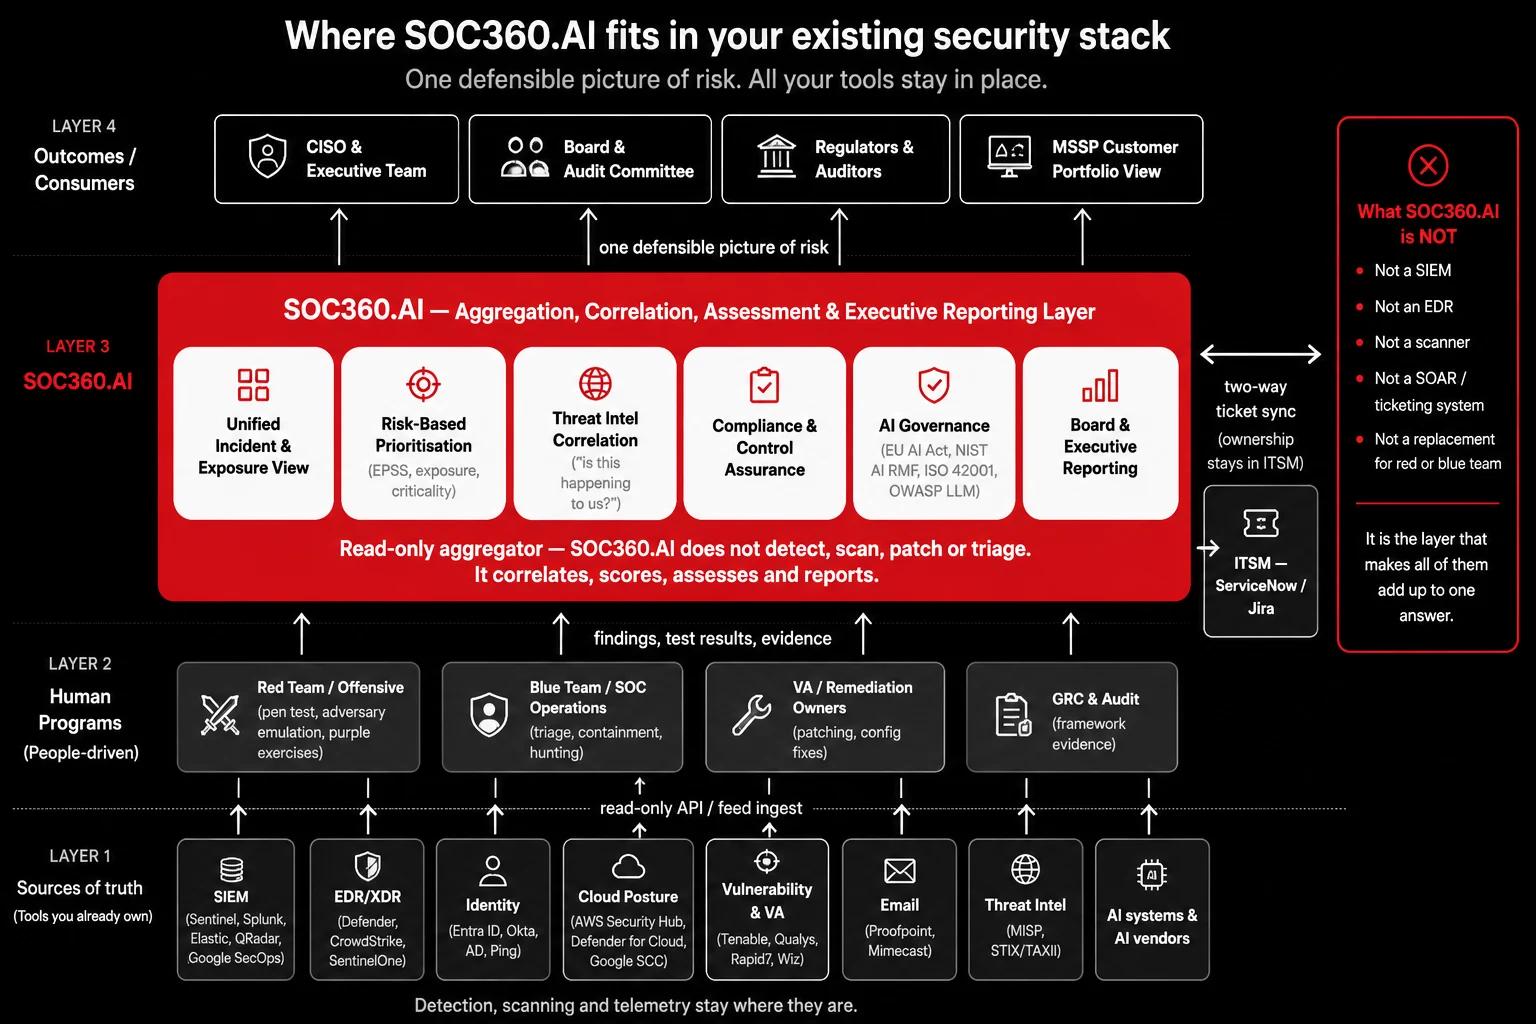
API and feed ingest from every source of truth: SIEM, EDR/XDR, identity, cloud posture, vulnerability management, email security, threat intel, and AI systems & vendors.
Red team, SOC, remediation owners and GRC keep doing what they do. SOC360.AI consumes their findings, test results and evidence.
Tickets sync both ways with ServiceNow and Jira. Ownership and workflow stay in your ITSM.
CISO and executive team, board and audit committee, regulators and auditors, and MSSP customer portfolios all consume the same defensible view.
Platform
Every incident, vulnerability and finding from every connected source — normalised into one pane and one data model, deduplicated and asset-linked.
Ranked by what actually matters: EPSS exploit probability, real exposure, and business criticality — not raw CVSS noise. Your teams fix the 2% that moves risk, not the 100% that fills a queue.
Answers the only intel question that matters: “Is this happening to us?” Live correlation of threat feeds against your own incidents, assets and exposures.
Continuous mapping of live evidence from your connected tools to your control frameworks — so you're always audit-ready, not audit-scrambling.
EU AI Act, NIST AI RMF, ISO 42001 and OWASP LLM Top 10 coverage for the AI systems and AI vendors in your environment — inventory, assessment, evidence and reporting as product, not consulting.
Board packs, regulator-ready reports and customer assurance documents generated from live data, with movement against the previous period — the same numbers your engineers see, in language your board understands.
Findings that share an IP, host, identity, domain, file hash or CVE collapse into one case with shared evidence, one owner and one status. Sixty business decisions instead of thousands of alerts.
Response deadlines and SLA clocks on every case, with notifications when work is about to slip — so it surfaces before it becomes a board question.
ServiceNow and Jira tickets stay in step in both directions. Your teams work where they always worked; the executive picture updates itself.
Per-customer retention by data type with archive-before-delete, scheduled snapshots, on-demand downloads and dry-run restore previews — evidence you can still produce a year later.
New regulatory surface
Your organisation is adopting AI systems and AI vendors faster than any spreadsheet can track. SOC360.AI treats them as first-class sources of truth — inventoried, assessed against EU AI Act, NIST AI RMF, ISO 42001 and OWASP LLM Top 10, and reported to your board in the same defensible picture as the rest of your risk.
Who it's for
Walk into every board meeting with one live, defensible picture of risk — and reclaim the analyst-weeks currently spent assembling it by hand.
Evidence-backed answers to “are we OK?”, trend lines you can challenge, and reporting that stands up to regulators and insurers.
Controls mapped to live evidence across every connected tool. Frameworks stay green because the data flows in, not because someone chased screenshots.
One portfolio-wide risk view across every customer, strict per-tenant isolation, and white-label reporting your clients will renew for.
SOC360.AI for MSSPs →Deployment
01
Read-only API and feed connections to your existing tools. No agents to install, no write access to grant, no change windows to book.
02
SOC360.AI normalises everything into one data model, deduplicates, links findings to assets, and scores risk with EPSS, exposure and business criticality.
03
Board packs, compliance evidence and executive dashboards flow from live data. Two-way ITSM sync keeps action where it belongs.
No rip-and-replace. No new attack surface. No quarter-long security review — because there's nothing to install and nothing we can touch.
Knowledge base
A 30-day rollout sequence, daily and weekly routines for each role, a plain-language tour of every workspace, a capability status list, and the handful of things only you can supply. Read it online or take the PDF.
FAQ
No — deliberately. SOC360.AI is not a SIEM, not an EDR, not a scanner and not a SOAR. Detection, scanning and telemetry stay exactly where they are. We're the layer that makes all of them add up to one answer.
SOC360.AI is read-only by design. No agents, no write access to your security tools, no ability to change configurations. The only two-way integration is ticket sync with your ITSM (ServiceNow / Jira), where ownership stays with your teams.
In your existing tools and teams. SOC360.AI prioritises and reports; your SOC, remediation owners and ITSM workflows act. Tickets sync both ways so status is always current in the executive picture.
Security and compliance frameworks for control assurance, plus dedicated AI governance coverage: EU AI Act, NIST AI RMF, ISO 42001 and OWASP LLM Top 10. Talk to us about the specific frameworks your organisation reports against.
Yes — MSSPs get a portfolio-wide view across all customers with strict per-tenant isolation and white-label reporting.
Because SOC360.AI is read-only and agentless, first connections are typically live in days, and most security reviews complete in weeks rather than quarters.
Less risk. Stronger control. Clearer answers — for every tool, team and AI system you already own.
We'll reply within one business day.